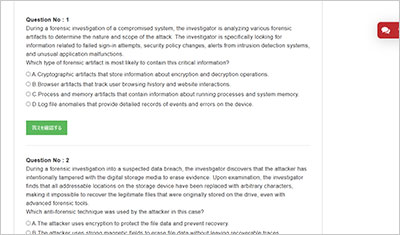
サンプル問題 1: In a financial institution's computer forensic investigation, suspicious activity reveals unauthorized access to GLBA (Gramm-Leach-Bliley Act)-protected customer data, raising concerns for customer safety. However, identifying the breach's source and extent poses significant challenges, complicating compliance with GLBA guidelines. What steps should be taken in a GLBA-covered computer forensic investigation when unauthorized access to sensitive customer data is discovered?
A: Ignore the incident if it does not directly threaten financial activities.
B: Share information with third parties for analysis.
C: Inform law enforcement without notifying affected customers.
D: Notify affected customers of opt-out rights and safeguard data.
正解:D
Explanation: According to CHFI v11 objectives under Computer Forensics Fundamentals and Regulations, Policies, and Ethics, a forensic investigator must ensure that technical investigation activities align with applicable legal and regulatory requirements. The Gramm-Leach-Bliley Act (GLBA) mandates that financial institutions protect customers’ nonpublic personal information (NPI) and respond appropriately to any unauthorized access or disclosure. When a breach involving GLBA-protected data is identified, the organization must follow a structured incident response and forensic investigation process while maintaining compliance with privacy laws. CHFI v11 emphasizes forensic readiness, legal compliance, and ethical handling of digital evidence. Notifying affected customers of their opt-out rights and implementing safeguards to protect compromised data are core requirements of GLBA’s Privacy Rule and Safeguards Rule. Ignoring the incident violates forensic and legal responsibilities, while sharing sensitive data with third parties risks further disclosure. Informing law enforcement alone is insufficient if customer notification obligations are not met. Proper customer notification demonstrates due diligence, supports transparency, and reduces legal risk. From a CHFI perspective, this approach ensures lawful evidence handling, regulatory compliance, and preservation of organizational credibility during forensic investigations
サンプル問題 2: Lucas, a forensic investigator, is working on an investigation involving a compromised hard drive. To analyze the disk image and extract relevant forensic data, he decides to use a tool that integrates the powerful capabilities of Sleuth Kit with Python scripting. Lucas wants to automate the process of analyzing disk structures, file systems, and file recovery using Python scripts. Which of the following tools can help Lucas leverage Sleuth Kit’s capabilities while using Python to perform these analysis tasks efficiently?
A: PyTSK
B: NumPy
C: PyTorch
D: PySpark
正解:A
Explanation: According to CHFI v11 objectives under Computer Forensics Fundamentals and Digital Forensics using Python, investigators are encouraged to automate forensic analysis tasks to improve efficiency, accuracy, and repeatability. The Sleuth Kit (TSK) is a widely used open-source forensic toolkit for analyzing disk images, file systems, and recovering deleted files. To extend these capabilities using Python, CHFI v11 highlights the use of Python bindings specifically designed for forensic purposes. PyTSK (also known as pytsk3) is the official Python binding for The Sleuth Kit. It allows forensic investigators to programmatically access disk images, partitions, file systems, directories, and file metadata directly from Python scripts. This enables automation of tasks such as file enumeration, timeline creation, deleted file recovery, and artifact extraction―core activities in disk and file system forensics. The other options are not suitable in this context. NumPy is designed for numerical computation, PyTorch is used for machine learning, and PySpark is intended for big data processing. None of these tools integrate with Sleuth Kit or provide native disk forensic analysis capabilities. Therefore, PyTSK is the correct and CHFI-aligned choice for Python-based Sleuth Kit forensic automation.
サンプル問題 3: During a federal investigation, a lawyer unintentionally discloses privileged information to a federal agency. The disclosure includes sensitive details related to a corporate client's ongoing legal dispute. In the scenario described, what conditions must be met for the unintentional disclosure to extend the waiver of attorney-client privilege or work-product protection to undisclosed communications in both federal and state proceedings?
A: The disclosed and undisclosed communications must concern different subject matters.
B: The waiver must be unintentional.
C: The disclosure must be accidental.
D: The waiver must be intentional, and the disclosed and undisclosed communications must concern the same subject matter.
正解:D
Explanation: This question aligns with CHFI v11 objectives related to legal compliance, rules of evidence, and handling privileged information during forensic investigations. In digital forensics, investigators frequently work alongside legal teams, making it critical to understand when attorney-client privilege or work-product protection may be waived. Under the U.S. Federal Rules of Evidence (Rule 502), an unintentional or inadvertent disclosure does not automatically extend the waiver of privilege to undisclosed communications. For a waiver to extend beyond the disclosed material, strict conditions must be met. The waiver must be intentional, the disclosed and undisclosed communications must concern the same subject matter, and fairness must require that the undisclosed information also be considered. CHFI v11 emphasizes that forensic investigators must preserve confidentiality, respect legal protections, and avoid actions that could improperly broaden legal exposure during investigations. Options B and C are incorrect because unintentional or accidental disclosures are explicitly protected from subject-matter waiver under Rule 502. Option A is incorrect because waiver extension only applies when communications involve the same subject matter. Therefore, Option D correctly reflects both legal standards and CHFI-aligned best practices for evidence handling and legal awareness during forensic investigations.