Digital Forensics in Cybersecurity サンプル問題プレビュー(抜粋)
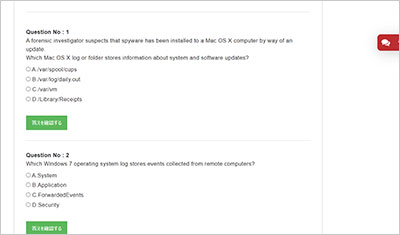
収録内容から抜粋したサンプル問題です。「解答・解説を表示」をクリックすると正解を確認できます。
サンプル問題 1: An organization believes that a company-owned mobile phone has been compromised. Which software should be used to collect an image of the phone as digital evidence?
A: PTFinder
B: Forensic SIM Cloner
C: Forensic Toolkit (FTK)
D: Data Doctor
正解:C
Explanation: Comprehensive and Detailed Explanation From Exact Extract: Forensic Toolkit (FTK) is a widely recognized and trusted software suite in digital forensics used to acquire and analyze forensic images of devices, including mobile phones. FTK supports the creation of bit-by-bit images of digital evidence, ensuring the integrity and admissibility of the evidence in legal contexts. This imaging process is crucial in preserving the original state of the device data without alteration. FTK enables forensic investigators to perform logical and physical acquisitions of mobile devices. It maintains the integrity of the evidence by generating cryptographic hash values (MD5, SHA-1) to prove that the image is an exact copy. Other options such as PTFinder or Forensic SIM Cloner focus on specific tasks like SIM card cloning or targeted data extraction but do not provide full forensic imaging capabilities. Data Doctor is more aligned with data recovery rather than forensic imaging. Reference: According to standard digital forensics methodologies outlined by NIST Special Publication 800-101 (Guidelines on Mobile Device Forensics) and the SANS Institute Digital Forensics and Incident Response guides, forensic tools used to acquire mobile device images must be capable of bit-stream copying with hash verification, which FTK provides
サンプル問題 2: A digital forensic examiner receives a computer used in a hacking case. The examiner is asked to extract information from the computer's Registry. How should the examiner proceed when obtaining the requested digital evidence?
A: Ensure that any tools and techniques used are widely accepted
B: Investigate whether the computer was properly seized
C: Enlist a colleague to witness the investigative process
D: Download a tool from a hacking website to extract the data
正解:A
Explanation: Comprehensive and Detailed Explanation From Exact Extract: In digital forensics, the use of reliable, validated, and widely accepted tools and techniques is critical to maintain the integrity and admissibility of digital evidence. According to the National Institute of Standards and Technology (NIST) guidelines and the Scientific Working Group on Digital Evidence (SWGDE) standards, any forensic process must utilize methods that are recognized by the forensic community and have undergone rigorous testing to ensure accuracy and reliability. Using validated tools helps prevent evidence contamination or loss and ensures that results can withstand legal scrutiny. While proper seizure and witnessing are important, the priority in the extraction phase is to use appropriate, trusted tools. Downloading tools from unauthorized or suspicious sources can compromise the evidence and is not an ethical or legal practice. Reference: NIST SP 800-101 (Guidelines on Mobile Device Forensics) and SWGDE Best Practices emphasize tool validation and adherence to community-accepted methods as foundational principles in forensic examination.
サンプル問題 3: A victim of Internet fraud fell for an online offer after using a search engine to find a deal on an expensive software purchase. Once the victim learned about the fraud, he contacted a forensic investigator for help. Which digital evidence should the investigator collect?
A: Virus signatures
B: Whois records
C: Computer logs
D: Email headers
正解:C
Explanation: Comprehensive and Detailed Explanation From Exact Extract: In Internet fraud investigations, computer logs are critical because they provide a record of user activity, including browsing history, downloads, and system events. These logs can help establish a timeline, identify malicious access, and confirm fraudulent transactions. Computer logs may include browser history, system event logs, and application logs that document the victim’s interaction with the fraudulent offer. Whois records help identify domain registration details but are secondary evidence. Email headers are relevant if communication via email was part of the fraud but less critical than logs that show direct interaction. Virus signatures are used in malware investigations, not directly relevant to fraud evidence collection. Reference: According to guidelines by the International Journal of Digital Crime and Forensics and the SANS Institute, capturing logs is essential in building a case for Internet fraud as it provides objective data about the victim’s system and activities.
WGU Digital Forensics in Cybersecurity試験準備をしていますか?それとも自分は全部できそうです。復習する必要がないと思いますか?それとも自分は何もできないような気がします。どうすればいいでしょうか?実は、この問題を解決するのは難しくないです。勉強者がやるべきのは分解分析をマスターすることです。ここではDigital Forensics in Cybersecurity問題集を使って学習中の課題を確認し、知識を整理してDigital Forensics in Cybersecurity (D431/C840) Course Exam試験の準備を進めます。
Digital Forensics in Cybersecurity問題集を利用して学習中の問題を探し出す。
WGU Digital Forensics in Cybersecurity試験のすべての試験資料ポイントを勉強した後、Digital Forensics in Cybersecurity問題集の中の問題点を練習してみてください。重要な試験点はどこにあるか、つまりWGUが把握してほしいものは何ですか?そして練習中の問題点を整理して分析してください。できない問題に対して、正しい答えの考えをはっきりさせたいです。それに関する知識点を明らかにします。間違った問題に対しては、具体的に自分がどこで間違っているかを見に行きます。このステップで使う試験資料ポイントは何ですか?間違った問題をこのように一歩分解して分析すると、自然に自分の復習する方向を見つけます。
その次に、非常規の試験ポイントのテーマは多すぎてこだわる必要はなくて、重要な試験点のテーマはきっと知識の点をわかります。特にDigital Forensics in Cybersecurity (D431/C840) Course Exam試験は試験資料ポイントが多いです。一つの問題は知識ポイントだけではなく、復習する時はまとめをマスターして、記憶を分類します。知識ポイントが覚えていないか、間違えていないかのために点数をなくしてはいけません。
Digital Forensics in Cybersecurity問題集を使って復習の効率を高めます。
Digital Forensics in Cybersecurity問題集を使って出題範囲に沿った練習問題に取り組み、自身の弱点を洗い出したうえで重点分野に絞った学習を強化します。確かに多くの復習方法の中で極めて有効な方法ですが、時間がかかります。実際の生活の中で私達の時間はいつも自分で支配しません。短い時間で復習の効率と質を向上させるには、毎回の復習に新しいものが必要です。どうやってできますか?
具体的な実践の方式は、Digital Forensics in Cybersecurity問題集のテーマを練習する時、まずテーマの題形を判断して、考察の知識点は同じタイプであれば、頭の中で一回だけ問題を解いたことがあります。見たことのない問題型については、一度真剣にやってみて、問題解決の構想と知識点を全力で理解して覚えてください。次の同じ問題型が現れたら、もう一度問題を解いたら、次の問題に直接飛び込むことができます。このようにジャンプして、モードの解答戦術を選んで、短い時間の内にDigital Forensics in Cybersecurity試験の覆うすべての知識ポイントのテーマをすべて一回通すことができます。それから、二回目、三回目はだんだん速くなります。正解率はますます高くなります。確かに、長い間勉強し続けていると、自分に嫌な気持ちになりやすいです。
この時、弊社はDigital Forensics in Cybersecurity問題集をいくつかの部分に分けて、一部分に時間を限定します。例えば、一時間でこれらの本を読み終わったり、8時までにこの章を完成したりします。これは復習の効率を高めるだけではなく、疲労感も生まれません。何度も頑張ってから、だんだん時間を短縮します。そのうち、一時間では終わらないことが分かります。今は四十分で完成します。上記のクイッククイズ方法に合わせて、Digital Forensics in Cybersecurity試験の内容を一週間でちゃんと復習ができます。